

Free Dec-2023 UPDATED Microsoft AZ-104 Exam Questions & Answer
Latest Success Metrics For Actual AZ-104 Exam Realistic Dumps
The Microsoft Azure Administrator certification exam consists of multiple-choice questions that are designed to evaluate the candidate's knowledge and understanding of various Azure services and features. It covers a wide range of topics such as Azure virtual machines, Azure storage, Azure networking, Azure security, Azure identity and access management, and Azure governance. AZ-104 exam is also designed to test the candidate's ability to troubleshoot common Azure issues and problems.
Microsoft AZ-104 Certification Exam is a valuable certification for IT professionals who want to validate their skills in administering Microsoft Azure services. Microsoft Azure Administrator certification is recognized globally and can help candidates advance their careers in cloud computing. To prepare for the exam, candidates can use various resources such as training courses, study guides, and practice exams.
NEW QUESTION # 119
You need to prepare the environment to meet the authentication requirements.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE Each correct selection is worth one point.
- A. an Azure Storage account and an access policy
- B. Azure Active Directory (AD) Identity Protection and an Azure policy
- C. a Recovery Services vault and a backup policy
- D. an Azure Key Vault and an access policy
Answer: D
Explanation:
Explanation
D: Seamless SSO works with any method of cloud authentication - Password Hash Synchronization or Pass-through Authentication, and can be enabled via Azure AD Connect.
B: You can gradually roll out Seamless SSO to your users. You start by adding the following Azure AD URL to all or selected users' Intranet zone settings by using Group Policy in Active Directory:
https://autologon.microsoftazuread-sso.com
NEW QUESTION # 120
You have an Azure subscription that contains the storage accounts shown in the following table.
You need to identify which storage account can be converted to zone-redundant storage (ZRS) replication by requesting a live migration from Azure support.
What should you identify?
- A. Storage1
- B. Storage3
- C. Storage2
- D. Storage4
Answer: C
Explanation:
Explanation
ZRS currently supports standard general-purpose v2, FileStorage and BlockBlobStorage storage account types.
NEW QUESTION # 121
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure Active Directory (Azure AD) tenant named Adatum and an Azure Subscription named Subscription1. Adatum contains a group named Developers. Subscription1 contains a resource group named Dev.
You need to provide the Developers group with the ability to create Azure logic apps in the Dev resource group.
Solution: On Subscription1, you assign the Logic App Operator role to the Developers group.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
The Logic App Operator role only lets you read, enable and disable logic app. With it you can view the logic app and run history, and enable/disable. Cannot edit or update the definition.
You would need the Logic App Contributor role.
Reference:
https://docs.microsoft.com/en-us/azure/role-based-access-control/built-in-roles
https://docs.microsoft.com/en-us/azure/logic-apps/logic-apps-securing-a-logic-app
NEW QUESTION # 122
You have an Azure subscription that contains a storage account named storage1.
You plan to use conditions when assigning role-based access control (RABC) roles to storage1 Which storage1 services support conditions when assigning roles?
- A. containers and queues only
- B. tables only
- C. queues only
- D. containers only
- E. file shares only
- F. files shares and tables only
Answer: D
Explanation:
Explanation
"Currently, conditions can be added to built-in or custom role assignments that have blob storage or queue storage data actions. "
https://learn.microsoft.com/en-us/azure/role-based-access-control/conditions-overview#where-can-conditions-be
NEW QUESTION # 123
You have an Azure subscription that contains the Azure virtual machines shown in the following table.
You add inbound security rules to a network security group (NSG) named NSG1 as shown in the following table.
You run Azure Network Watcher as shown in the following exhibit.
You run Network Watcher again as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 124
You have an Azure Active Directory (Azure AD) tenant named adatum.com. Adatum.com contains the groups in the following table.
You create two user accounts that are configured as shown in the following table.
To which groups do User1 and User2 belong? To answer. select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 125
You are evaluating the connectivity between the virtual machines after the planned implementation of the Azure networking infrastructure.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/virtual-network/virtual-network-peering-overview
https://docs.microsoft.com/en-us/azure/networking/networking-overview#internet-connectivity
NEW QUESTION # 126
You have an Azure subscription that contains a virtual network named VNET in the East Us 2 region. A network interface named VM1-NI is connected to VNET1.
You successfully deploy the following Azure Resource Manager template.
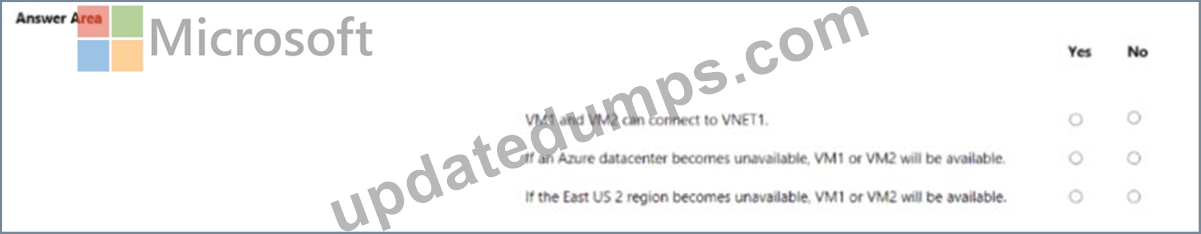
Answer:
Explanation:
NEW QUESTION # 127
You need to define a custom domain name for Azure AD to support the planned infrastructure.
Which domain name should you use?
- A. humongousinsurance.com
- B. humongousinsurance.onmicrosoft.com
- C. ad.humongousinsurance.com
- D. humongousinsurance.local
Answer: A
Explanation:
Every Azure AD directory comes with an initial domain name in the form of domainname.onmicrosoft.com.
The initial domain name cannot be changed or deleted, but you can add your corporate domain name to Azure AD as well. For example, your organization probably has other domain names used to do business and users who sign in using your corporate domain name. Adding custom domain names to Azure AD allows you to assign user names in the directory that are familiar to your users, such as '[email protected].' instead of 'alice@domain name.onmicrosoft.com'.
Scenario:
Network Infrastructure: Each office has a local data center that contains all the servers for that office. Each office has a dedicated connection to the Internet.
Humongous Insurance has a single-domain Active Directory forest named humongousinsurance.com Planned Azure AD Infrastructure: The on-premises Active Directory domain will be synchronized to Azure AD.
References:
https://docs.microsoft.com/en-us/azure/active-directory/fundamentals/add-custom-domain
NEW QUESTION # 128
You are the global administrator for an Azure Active Directory (Azure AD) tenant named adatum.com.
You need to enable two-step verification for Azure users.
What should you do?
- A. Enable Azure AD Privileged Identity Management.
- B. Configure a playbook in Azure Security Center.
- C. Create an Azure AD conditional access policy.
- D. Install and configure Azure AD Connect.
Answer: C
Explanation:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-mfa-getstarted
NEW QUESTION # 129
You have the Azure virtual machines shown in the following table.
A DNS service is install on VM1.
You configure the DNS server settings for each virtual network as shown in the following exhibit.
You need 10 ensure that all the virtual machines can resolve DNS names by using the DNS service on VM1.
What should you do?
- A. Add service endpoints on VNET1.
- B. Add service endpoints on VNET2 and VNET3.
- C. Configure peering between VNE11, VNETT2, and VNET3.
- D. Configure a conditional forwarder on VM1
Answer: C
Explanation:
Explanation
An Azure AD DS DNS zone should only contain the zone and records for the managed domain itself.
A conditional forwarder is a configuration option in a DNS server that lets you define a DNS domain, such as contoso.com, to forward queries to. Instead of the local DNS server trying to resolve queries for records in that domain, DNS queries are forwarded to the configured DNS for that domain. This configuration makes sure that the correct DNS records are returned, as you don't create a local a DNS zone with duplicate records in the managed domain to reflect those resources.
To create a conditional forwarder in your managed domain, complete the following steps:
1. Select your DNS zone, such as aaddscontoso.com.
2. Select Conditional Forwarders, then right-select and choose New Conditional Forwarder...
3. Enter your other DNS Domain, such as contoso.com, then enter the IP addresses of the DNS servers for that namespace, as shown in the following example:
4. Check the box for Store this conditional forwarder in Active Directory, and replicate it as follows, then select the option for All DNS servers in this domain, as shown in the following example:
5. To create the conditional forwarder, select OK.
Name resolution of the resources in other namespaces from VMs connected to the managed domain should now resolve correctly. Queries for the DNS domain configured in the conditional forwarder are passed to the relevant DNS servers.
Reference:
https://docs.microsoft.com/en-us/azure/virtual-network/virtual-networks-name-resolution-for-vms-and-role-insta
https://docs.microsoft.com/en-us/azure/active-directory-domain-services/manage-dns
NEW QUESTION # 130
You plan to create an Azure Storage account in the Azure region of East US 2.
You need to create a storage account that meets the following requirements:
Replicates synchronously
Remains available if a single data center in the region fails
How should you configure the storage account? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/storage/common/storage-redundancy
https://docs.microsoft.com/en-us/azure/storage/common/storage-redundancy-zrs
NEW QUESTION # 131
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure subscription that contains the resources shown in the following table.
VM1 connects to VNET1.
You need to connect VM1 to VNET2.
Solution: You turn off VM1, and then you add a new network interface to VM1.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
Instead you should delete VM1. You recreate VM1, and then you add the network interface for VM1.
Note: When you create an Azure virtual machine (VM), you must create a virtual network (VNet) or use an existing VNet. You can change the subnet a VM is connected to after it's created, but you cannot change the VNet.
Reference:
https://docs.microsoft.com/en-us/azure/virtual-machines/windows/network-overview
NEW QUESTION # 132
You plan to create an Azure virtual machine named VM1 that will be configured as shown in the following exhibit.
The planned disk configurations for VM1 are shown in the following exhibit.


You need to ensure that VM1 can be created in an Availability Zone.
Which two settings should you modify? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Availability options
- B. OS disk type
- C. Use managed disks
- D. Size
- E. Image
Answer: C,E
NEW QUESTION # 133
You have an Azure Service Bus.
You need to implement a Service Bus queue that guarantees first in first-out (FIFO) delivery of messages.
What should you do?
- A. Set the Lock Duration setting to 10 seconds.
- B. Enable partitioning.
- C. Enable duplicate detection.
- D. Enable sessions.
- E. Set the Max Size setting of the queue to 5 GB.
Answer: D
Explanation:
Explanation
Through the use of messaging sessions you can guarantee ordering of messages, that is first-in-first-out (FIFO) delivery of messages.
References:
https://docs.microsoft.com/en-us/azure/service-bus-messaging/service-bus-azure-and-service-bus-queues-compa
NEW QUESTION # 134
You create an Azure web app named WebApp1. WebApp1 has the autoscale settings shown in the following exhibit.

The scale out and scale in rules are configured to have a duration of 10 minutes and a cool down time of five minutes.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Box 1: one instance
Refer to scaling condition provided in the question, August 8, 2018 is outside the schedule of the scale condition 1, and Default instance count is 1.
Box 2: two instances
The default instance count is important because autoscale scales your service to that count when metrics are not available. Therefore, select a default instance count that's safe for your workloads.
The Default instance count of scale condition 1 is 4, and the Scale in rule decreases the count with 1.
So initial instance count before scale in condition met = 4
CPU utilization was at 15% for 60 mins so after first 10 mins ( The scale out and scale in rules are configured to have a duration of 10 minutes )instance count reduces by 1 hence after first 10 mins instance count is 4-1=3 Now cool down period is 5 mins , after first 15 mins instance count is 3 .
After next 15 mins , instance count will be 3-1=2.
After next 15 mins , instance count will be =2 because minimum instance count must be 2 , it can't get reduced beyond 2.
So after 60 mins instance count will be at 2.
Reference:
https://docs.microsoft.com/en-us/azure/azure-monitor/platform/autoscale-best-practices
NEW QUESTION # 135
You have an Azure Active Directory tenant named Contoso.com that includes following users:
Contoso.com includes following Windows 10 devices:
You create following security groups in Contoso.com:
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: Yes
User1 is a Cloud Device Administrator.
Device2 is Azure AD joined.
Group1 has the assigned to join type. User1 is the owner of Group1.
Note: Assigned groups - Manually add users or devices into a static group.
Azure AD joined or hybrid Azure AD joined devices utilize an organizational account in Azure AD Box 2: No User2 is a User Administrator.
Device1 is Azure AD registered.
Group1 has the assigned join type, and the owner is User1.
Note: Azure AD registered devices utilize an account managed by the end user, this account is either a Microsoft account or another locally managed credential.
Box 3: Yes
User2 is a User Administrator.
Device2 is Azure AD joined.
Group2 has the Dynamic Device join type, and the owner is User2.
References:
https://docs.microsoft.com/en-us/azure/active-directory/devices/overview
NEW QUESTION # 136
You create a virtual machine scale set named Scale1. Scale1 is configured as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
Answer:
Explanation:
References:
https://docs.microsoft.com/en-us/azure/azure-monitor/platform/autoscale-overview
https://docs.microsoft.com/en-us/azure/azure-monitor/platform/autoscale-best-practices
https://docs.microsoft.com/en-us/azure/azure-monitor/platform/autoscale-common-scale-patterns
NEW QUESTION # 137
You implement the planned changes for NSG1 and NSG2.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Graphical user interface, text, application, email Description automatically generated
NEW QUESTION # 138
You have an Azure subscription that contains a storage account.
You have an on-premises server named Server1 that runs Window Server 2016. Server1 has 2 TB of data.
You need to transfer the data to the storage account by using the Azure Import/Export service.
In which order should you perform the actions? To answer, move all actions from the list of actions to the answer area and arrange them in the correct order.
NOTE: More than one order of answer choices is correct. You will receive credit for any of the correct orders you select.
Answer:
Explanation:
At a high level, an import job involves the following steps:
Step 1: Attach an external disk to Server1 and then run waimportexport.exe Determine data to be imported, number of drives you need, destination blob location for your data in Azure storage.
Use the WAImportExport tool to copy data to disk drives. Encrypt the disk drives with BitLocker.
Step 2: From the Azure portal, create an import job.
Create an import job in your target storage account in Azure portal. Upload the drive journal files.
Step 3: Detach the external disks from Server1 and ship the disks to an Azure data center.
Provide the return address and carrier account number for shipping the drives back to you.
Ship the disk drives to the shipping address provided during job creation.
Step 4: From the Azure portal, update the import job
Update the delivery tracking number in the import job details and submit the import job.
The drives are received and processed at the Azure data center.
The drives are shipped using your carrier account to the return address provided in the import job.
References:
https://docs.microsoft.com/en-us/azure/storage/common/storage-import-export-service
NEW QUESTION # 139
You have an Azure virtual machine named VM1 that runs Windows Server 2019.
You save VM1 as a template named Template1 to the Azure Resource Manager library.
You plan to deploy a virtual machine named VM2 from Template1.
What can you configure during the deployment of VM2?
- A. administrator username
- B. operating system
- C. virtual machine size
- D. resource group
Answer: A
Explanation:
When deploying a virtual machine from a template, you must specify:
- the Resource Group name and location for the VM
- the administrator username and password
- an unique DNS name for the public IP
Reference:
https://docs.microsoft.com/en-us/azure/virtual-machines/windows/ps-template
NEW QUESTION # 140
You manage an Azure Windows Server virtual machine (VM) that hosts several SQL Server databases.
You need to configure backup and retention policies for the VM. The backup policy must include transaction log backups.
What should you do?
- A. Configure a point-in-time snapshot from the Disks Azure portal blade.
- B. Configure a continuous delivery deployment group from the Virtual Machine Azure portal blade.
- C. Configure a SQL Server in Azure VM backup policy from the Recovery Services Azure portal blade.
- D. Configure point-in-time and long-term retention policies from the SQL Servers Azure portal blade.
Answer: C
Explanation:
You should configure a SQL Server in Azure VM backup policy from the Recovery Services Azure portal blade.
The Azure Recovery Services vault has three default policy templates:
Azure Virtual Machine
Azure File Share
SQL Server in Azure VM
Because you need to back up both the SQL Server databases as well as transaction logs, you should create a SQL Server in Azure VM backup policy. These policies also enable you to specify backup retention durations at the daily, weekly, monthly, and yearly scopes.
You should not configure point-in-time and long-term retention policies from the SQL Servers Azure portal blade. These backup and retention policies are available for the Azure SQL Database platform-as-a-service (PaaS) offering, and not for Azure virtual machines hosting SQL Server databases.
You should not configure a continuous delivery deployment group from the Virtual Machine Azure portal blade. This feature is unrelated to VM backup and recovery, and allows you to integrate a VM in a Visual Studio Team Services (VSTS) continuous integration/continuous deployment (Cl/CD) workflow.
You should not configure a point-in-time snapshot from the Disks Azure portal blade. The snapshot functionality in Azure does not have formal policy associated with it, nor does it back up VM configuration.
NEW QUESTION # 141
You need to configure the Device settings to meet the technical requirements and the user requirements.
Which two settings should you modify? To answer, select the appropriate settings in the answer area.
Answer:
Explanation:
NEW QUESTION # 142
......
Certification Overview
Those who manage to garner success in AZ-104 exam will be awarded the Microsoft Certified: Azure Administrator Associate certification. This is an excellent pick that an Azure professional can make to gain real-time management competencies and become a suitable candidate for administration job roles.
With the help of expanded exam modules, this certificate permeates the applicants with the latest cognizance about Azure governance and management, virtual networks, identities, and storage-related topics. Furthermore, expertise in the resource adjustment and monitoring, under a given situation, can be acquired by the time the training process ends.
Updated AZ-104 Dumps Questions For Microsoft Exam: https://prepaway.updatedumps.com/Microsoft/AZ-104-updated-exam-dumps.html